Assess your data controls and identify implementation gaps.
Burhan inspects data sources to identify personal fields and their protection status, then assesses applicable PDPL, NDMO and SDAIA controls. It presents gaps, evidence and proposed remediation for specialist review, not legal certification. Installed on your premises, it works offline.
- Automated scanning of actual data sources
- Compliance score per framework: PDPL, NDMO, SDAIA
- PII discovery and gap analysis with a remediation plan
- On-premises install that works offline
Connected data sources
5 sources · 1.2M records scanned
86%
control assessment score · illustrative
- PDPLPersonal Data Protection Law92%
- NDMOData management controls78%
- SDAIAAI ethics principles85%
PII discovery
Found 3 unprotected columns holding national IDs and phone numbers in the HR database, and suggested encryption and masking.
- to notify SDAIA of a breach
- 72 hours
- one score per framework, down to the requirement
- PDPL · NDMO · SDAIA
- offline, never trains public models
- On-premises
Presentation
Burhan · Product deck
Prove PDPL, NDMO and SDAIA compliance on your real data
Read the presentation· slide by slide, with the presenter's notes
1. Burhan
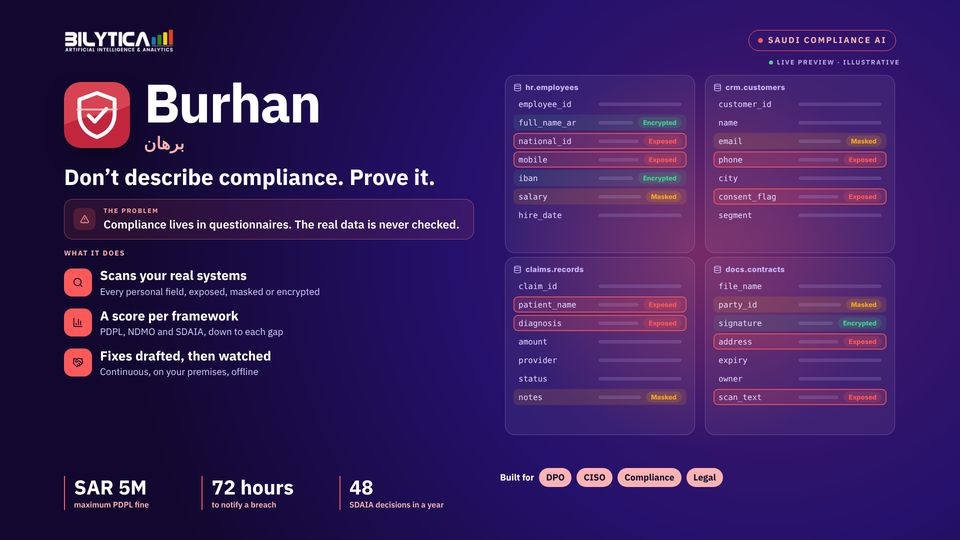
This is Burhan, برهان, which means proof. Burhan scans your real systems, finds every personal field and shows how it is protected: exposed, masked or encrypted. Then it proves where you stand on PDPL, NDMO and SDAIA. Don’t describe compliance; prove it.
2. A breach is found. The clock starts.
Let me show the problem against the clock. A breach is found and the clock starts: PDPL gives you 72 hours to notify SDAIA. Hour four: which systems hold national IDs? Nobody is sure. Hour eighteen: last year’s questionnaire lists four systems; there are eleven. Hour thirty-six: IT exports table lists by hand. Hour fifty-eight: was it encrypted? It depends who you ask. Hour seventy: an estimate goes to leadership. This is illustrative, but the gap is real.
3. The policy exists. The evidence does not.
Why does it happen? Because the policy exists, but the evidence does not. The questionnaire says national IDs are encrypted; the data shows them in plain text. It says consent is recorded; the consent field is empty for a third of customers. Questionnaires describe the data. Burhan looks at it.
4. Continuous, not once a year
Burhan is installed on your premises and works offline. It connects to your databases, warehouses, CRM and documents; discovers every personal field with a confidence score; scores each framework down to the requirement; ranks each gap with its legal reference; drafts the fix; and alerts the moment a score drops. Continuous, not once a year.
5. One score per framework, and the gaps to close
This is what leadership sees: one score per framework, and the gaps to close, each tied to its framework and ranked by severity, with the fix drafted and the evidence recorded. The figures here are illustrative.
6. Compliance is now a business risk
Why now? PDPL enforcement has been active since the grace period ended on 14 September 2024. Fines reach SAR 5 million per violation and can be doubled for repeats. You have 72 hours to notify SDAIA of a breach. SDAIA issued 48 enforcement decisions in one year. And the same governance practice that cut supervisory reporting time 85% at a central bank is built into Burhan.
7. A compliance tool that adds no risk
A compliance tool must not add risk. Burhan is installed on your premises, inside your walls. It works offline, never trains public models, and writes its reports and policies in regulatory Arabic and English. It is built by Bilytica in Riyadh.
8. Prove your compliance from your own data.
So here is the question to leave you with: could you show a regulator, today, where your customers’ personal data lives and how it is protected? Let’s find out together. Connect one database, warehouse or CRM, scanned on your premises. See your real position: a score per framework, the personal data found and the gaps ranked. Then approve the drafted fixes and monitor continuously. Write to us at sales@bilytica.sa. Thank you.
How it works
From data sources to a control assessment report for specialist review
In
Data sources
- HR database
- Analytics warehouse
- CRM
- Documents
Installed on-premises, works offline.
Scan
Compliance engine
Out
Compliance report
- PDPL92%
- NDMO78%
- SDAIA85%
- 01
Connect data sources
Databases, warehouses, CRM and documents, through a guided wizard.
- 02
Scan and discover
Schemas and records scanned; personal and sensitive fields found with confidence scores.
- 03
Assess control implementation
A control implementation assessment score for PDPL, NDMO and SDAIA principles, broken down by requirement.
- 04
Analyse gaps
Every gap tied to the relevant article or control and ranked by severity.
- 05
Remediate and monitor
An AI assistant drafts policies and fixes, and continuous monitoring alerts on any regression.
What changes
The policy exists. The evidence does not. Burhan looks at the data itself, continuously, not once a year.
Compliance questionnaires filled in by hand
Automated scanning of actual data sources
Personal data nobody can locate
Automatic PII discovery with confidence scores
Gaps found at the external audit
A continuous gap board with a remediation plan
Data leaving the building for assessment
Installed on your premises, works offline
It sees your data as it is, not as it is described
The product connects to databases, warehouses and documents, scans schemas and records, discovers personal data fields such as national ID, phone and email with confidence scores, and checks the protection applied to each.
- Guided connection wizard for databases, warehouses, Salesforce and documents
- PII and confidential field discovery with per-field confidence
- Protection status per field: encrypted, masked or exposed
- Scan history with automatic scheduling
Connected data sources
5 sources · 1.2M records scanned
86%
control assessment score · illustrative
- PDPLPersonal Data Protection Law92%
- NDMOData management controls78%
- SDAIAAI ethics principles85%
PII discovery
Found 3 unprotected columns holding national IDs and phone numbers in the HR database, and suggested encryption and masking.
Every gap has a legal reference and a fix plan
Gaps are shown ranked by severity, each tied to the relevant article or control. The remediation assistant suggests steps and drafts policies, and the audit hub prepares evidence for the regulator.
- Gaps ranked by severity and tied to legal articles
- AI assistant that writes policies and remediation steps
- Audit hub with an evidence trail ready for review
- Continuous monitoring with alerts on compliance drops
- High
Consent records incomplete
PDPL · Article 5
- Medium
Data retention policy missing
NDMO · Retention policy
- Medium
Processing register out of date
PDPL · Processing register
Capabilities
A full compliance system, not a checklist
Data source connections
Databases, warehouses, CRM and documents in one board.
PII discovery
Finds national ID, phone, email and more, with confidence scores.
Score per framework
PDPL, NDMO and SDAIA, broken down to each requirement.
Gap analysis
Gaps ranked by severity and tied to legal articles.
Remediation assistant
Suggests fixes and drafts policies in regulatory Arabic.
Policy generator
Draft privacy, retention and processing policies for specialist review before approval.
Audit hub
Evidence and activity trail ready for internal and external review.
Continuous monitoring
Alerts when unprotected data appears or scores drop.
On-premises install
Runs on your infrastructure with no internet connection.
Data never leaves
All scanning happens inside your environment; your data never trains public models.
Made in Saudi Arabia
From actual data to a clear gap and reviewable evidence.
Burhan was built in Riyadh around Saudi regulation specifically: the Personal Data Protection Law, National Data Management Office controls, and SDAIA's AI ethics principles.
- PDPL, NDMO and SDAIA frameworks built in and kept current
- On-premises install, your data never leaves
- Reports and policies in regulatory Arabic
- Built and supported by a Saudi team
Comparison
How Burhan is different
| Capability | Generic GRC tools | Burhan |
|---|---|---|
| PDPL, NDMO and SDAIA frameworks built in | · | |
| Scans actual data sources, not questionnaires | Partial | |
| PII discovery in Arabic and English data | · | |
| Remediation assistant that drafts policies | · | |
| On-premises, offline installation | · |
Integrations
Connects to wherever your data lives
Connected systems
- ERP
- CRM
- Portals
- Partners
Integration layer
- Secure APIs
- Validation on entry
- Retry and alerting
Data checked on the way
Date 12/05/24 · 2024-05-12One date format
Every system sees the same record
- Source tracked
- Change logged
Frequently asked questions
What is Bilytica Burhan?+
A Saudi-built product that connects to your data sources and checks compliance with PDPL, NDMO controls and SDAIA principles, with PII discovery, gap analysis and a remediation plan. It installs on your premises and works offline.
How does it check compliance?+
You connect data sources such as databases, warehouses and CRM systems. It scans schemas and records, identifies personal data fields, and presents control implementation status with a breakdown of gaps. Scan results are not regulatory certification or a substitute for specialist review.
Does it work without internet?+
Yes. It installs on your infrastructure on-premises, and all scanning and analysis happens locally, so your data never leaves your environment.
Which frameworks are covered?+
The Personal Data Protection Law (PDPL), National Data Management Office (NDMO) controls, and SDAIA AI ethics principles, with the option to add others such as GDPR.
Does it only report, or does it help fix gaps?+
It helps fix them. Every gap is tied to the legal article and ranked by severity, the remediation assistant suggests steps and drafts policies, and continuous monitoring watches after the fix.
Who needs this product?+
Compliance, data governance and cybersecurity teams in government entities and companies that process personal data or fall under NDMO controls.
Assess controls against your own data.
Could you show a regulator, today, where your customers' personal data lives and how it is protected? Connect one database, warehouse or CRM and see a score per framework, the personal data found and the gaps ranked.